Business phone system
- Cloud featuresCall routing, IVR, queues, recording and voicemail to email
- Desktop and mobile appsCalls, SMS, team chat and video meetings in one app
- AI phone agents Built inAnswer every call, book jobs and take messages 24/7
- 90s is callingStill on an old PBX? Here is what you are missing
- International call ratesPer-minute rates to every country we call
Apps and internet
- Desktop app Live demoCalls, chat, SMS and AI summaries in one window
- Mobile app Live demoYour business number on your iPhone or Android
- Why our internetBuilt for voice, so calls stay clear when the line is busy
- NBN for businessBusiness NBN set up alongside your phones
- SUPA InternetFast fibre for buildings on the SUPA network
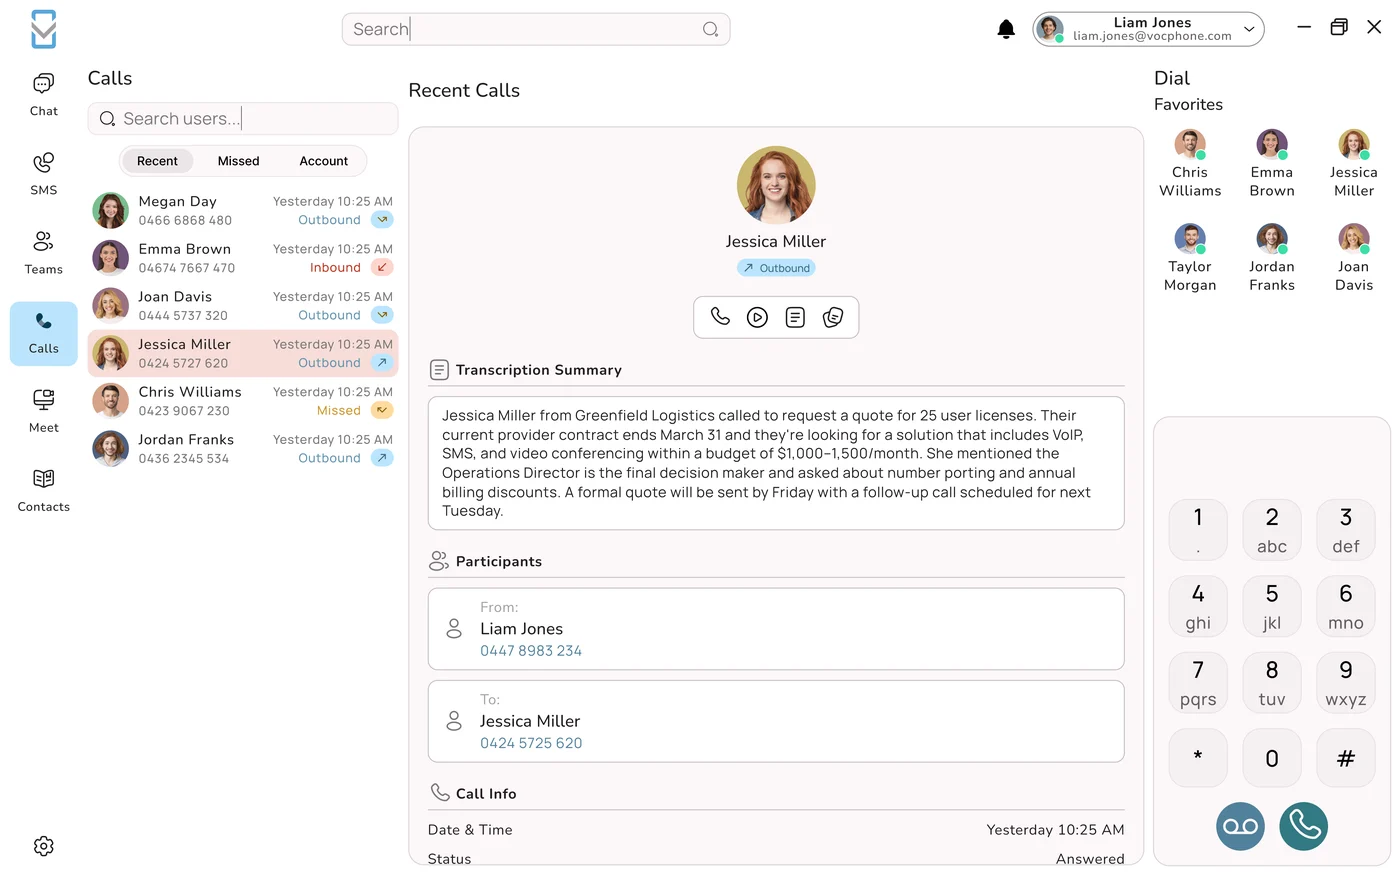
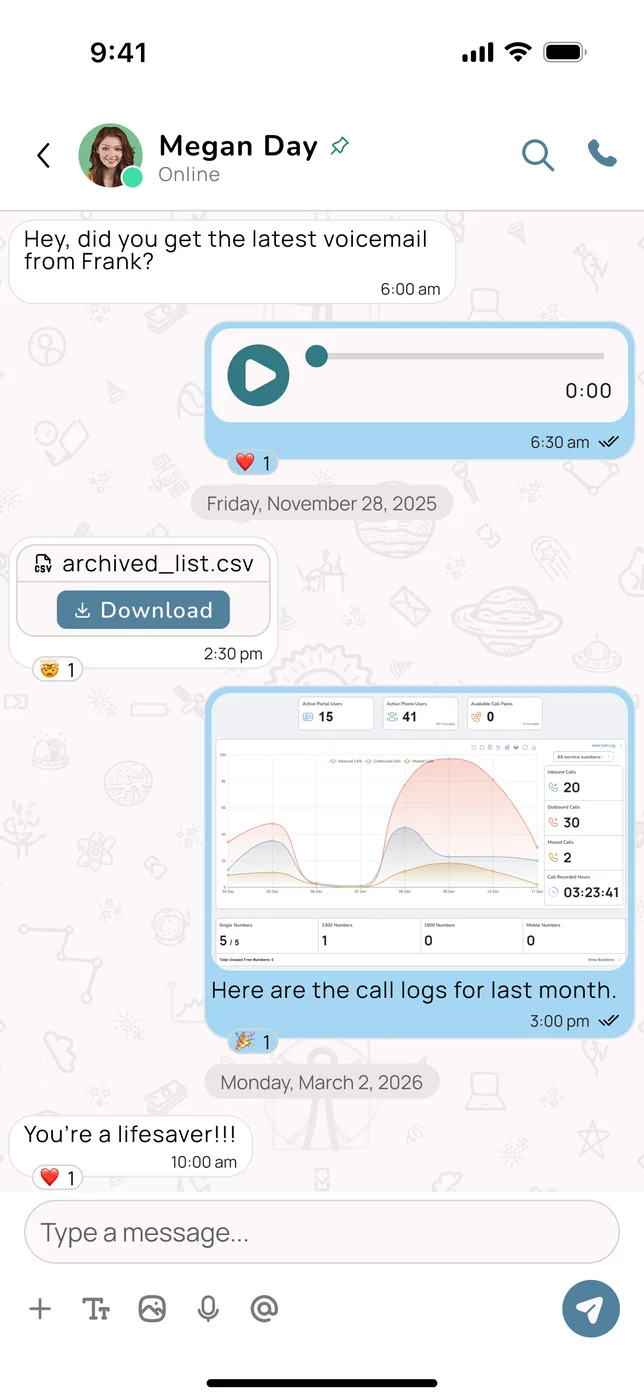
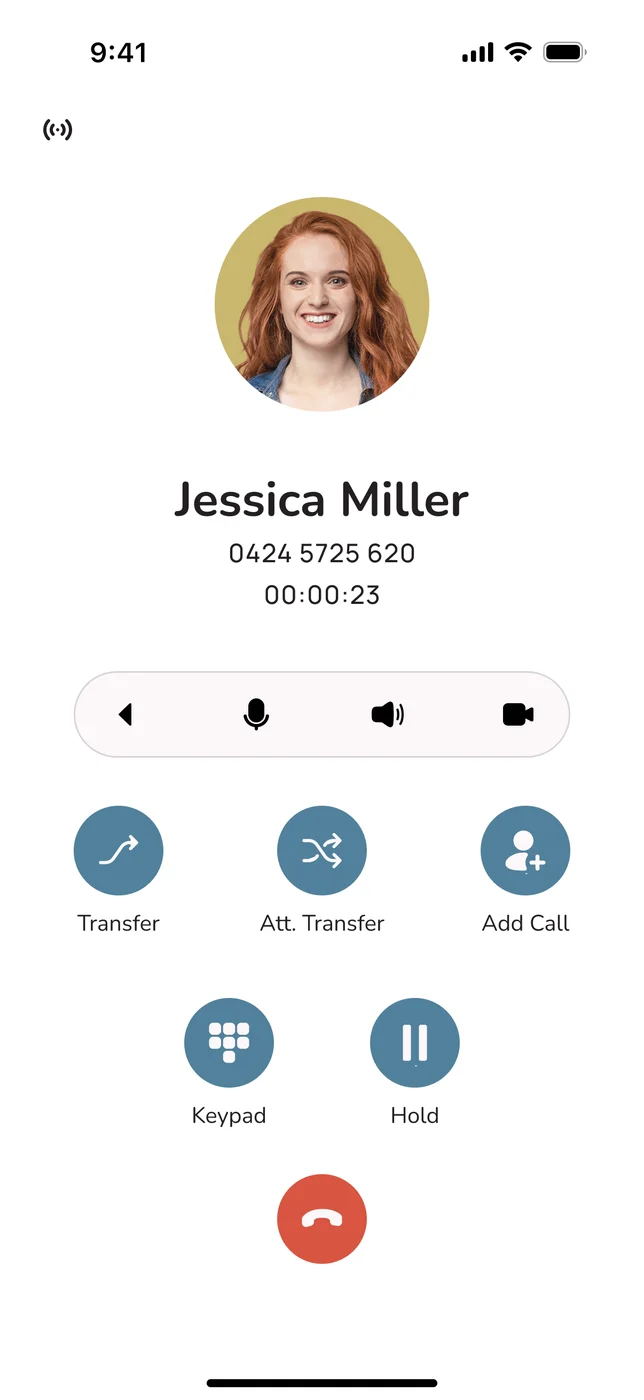
New Try it liveTake the VOCPhone apps for a spin, right here
Click through working demos of the desktop and mobile apps: calls with AI summaries, team chat, SMS and more. No download, no sign up.
Desktop app demoMobile app demoOur own network, not a reseller's. 99.99% uptime and support from our team in Australia.Book a demoAll features
AI on your phone line
VOCPhone vs AI receptionists
See every comparisonAI AgentsEvery call answered, day or night
It picks up with a natural Aussie accent, answers questions, books the job and sends you the summary.
Meet your AI agentBuilt into your phone system, not bolted on. No extra number, no call forwarding.Book a demo
Professional services
Trades, retail and hospitality
Browse all industries
Our customersFrom one-person shops to national brands
See how businesses like yours set up their phones.
Find your industryWorking on your own? We have plans made for sole traders and freelancers too.Self-employedStartups
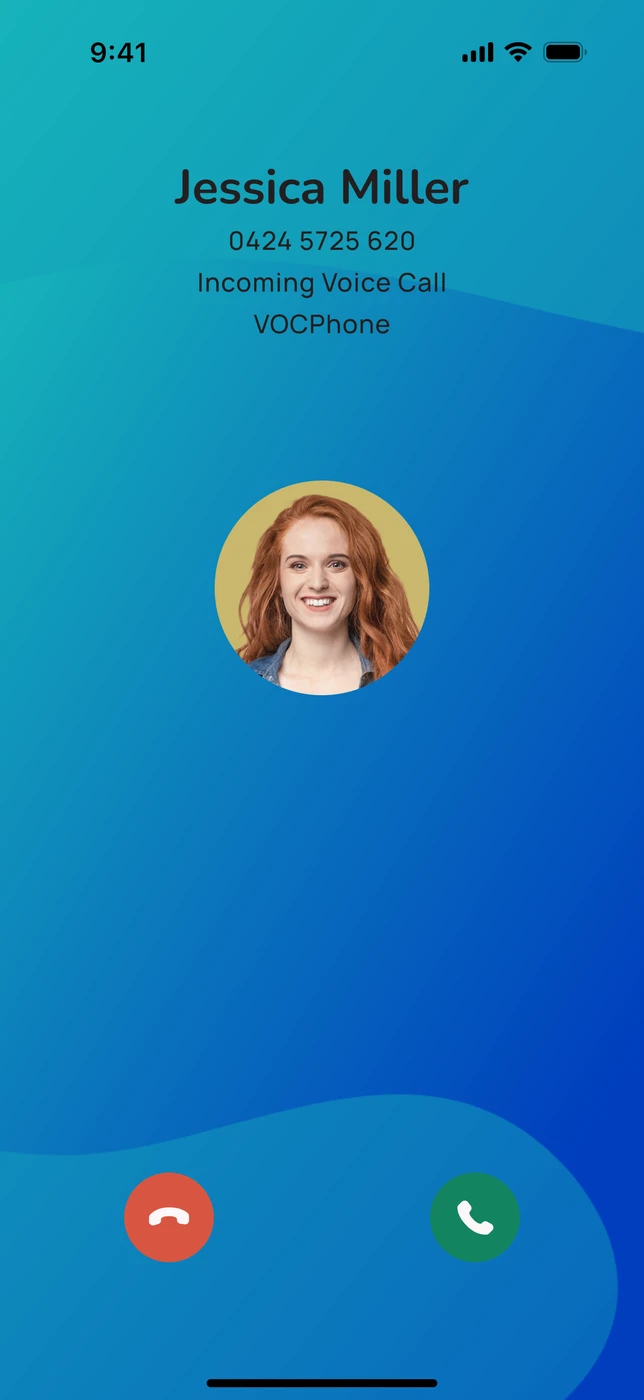
Voice plansBusiness phone planfrom$84.90/month3 users included on a 36-month term, then $30 per extra user.Free setup and free number portingDesktop and mobile apps includedAI Agents built inSee voice plans![Incoming call in the VOCPhone mobile app]()
![Friends watching a sunset]()
Internet and more
- Voice plansBusiness phone plans from $84.90 a month, 3 users included
- HardwareHandsets, headsets, conference phones and accessories
- NBN InternetBusiness NBN from the team that runs your phones
- SUPA InternetFibre plans for buildings on the SUPA network
- Upload your billWe send a written comparison within one business day
Bundle and savePhones and internet from one Aussie team
One provider to call when something needs fixing. No finger pointing.
Compare all plansMonth-to-month plans available. Keep your existing numbers when you move across.Sign up online1300 663 222
Learn and get set up
The library at a glanceBrowse all
147business
guides530kreads
so far
guides530kreads
so far
Guides by topic
- Phone systems55
- AI22
- NBN14
- Industries8
- Costs6
- Security4
- News2
- Other guides36
Need a hand? Our support team is based in Australia, with AI agents answering after hours.Contact support
Call us on 1300 663 222 or send a message and the team will get back to you.Send a message
Benefits of Voice over Cloud
Practical guides to business phone systems, cloud PBX, AI call handling and the Australian telco rules that affect them. Written for the people who actually run the phones, and updated as the rules and the technology change.